Seonglae Cho
Theorem prover
Leanstral
Seed-Prover
Formal languages like Lean enable automatic verification, making them advantageous for reinforcement learning (RL) through Lemma-Style Proving: proving intermediate lemmas first → utilizing them for main theorems, and Iterative Refinement: iteratively improving proofs using Lean feedback, self-summarization, and leveraging previous proofs.
FormalQualBenchp
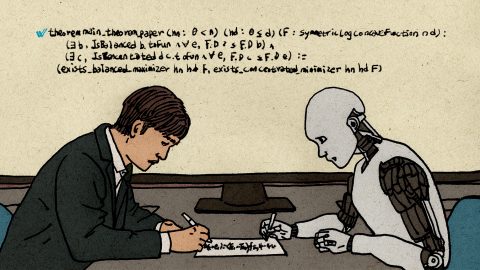


Leonardo de Moura

Don't believe everything
- Soundness bugs: bugs have been found in the Lean4 kernel that allow false propositions to be proved, raising concerns that AI could exploit such vulnerabilities.
- Mathematical consistency: the author argues that the consistency of the official Lean4 type theory has not yet been proven.
- Nested inductive types: complex recursive structures may be the main source of both theoretical and implementation-level vulnerabilities.
- con-leche: a separate verification kernel was built, but it does not guarantee the safety of the official Lean4 kernel.
- Anthropic's Fermat's Last Theorem: criticism of the decision to disable the sandbox while verifying AI-generated proofs. That said, the author notes that they re-verified it with the sandbox enabled and it passed.